
81·
9 days agoThat they are building an anti-cheat with existing open kernel security features instead of writing their own kernel modules is somehow a bad thing?
That they are building an anti-cheat with existing open kernel security features instead of writing their own kernel modules is somehow a bad thing?

Realistically your best option is a CDN with some layer of bot detection and blocking. Cloudflare is of course the most popular choice, https://bunny.net/ might also work but I haven’t tried their advanced Shield level so not sure how good it is.
Some commercial advanced firewall / WAF might also be an option. Seems most of them has Bot mitigation features, but I haven’t tried their never personally tried anything like that.
To be honest I haven’t done that deep search into how common it is for VPS providers to block port 25, but in the cases it has been relevant for me it has required at least raising a request and for instance for Hetzner being a customer for at least one month. I’ve figured that it’s a good thing and if a VPS provider has no restrictions at all their IP ranges are much more likely to have bad reputation and blocklist issues.
The big problem you’ll run into is that it’s very likely outgoing connections to port 25 is blocked. In my experience it’s very uncommon that residential ISPs allow it, and even most VPS providers will block it unless you request access. So you’ll most likely need some form of relay anyway, and at that point you may as well send directly to the relay.
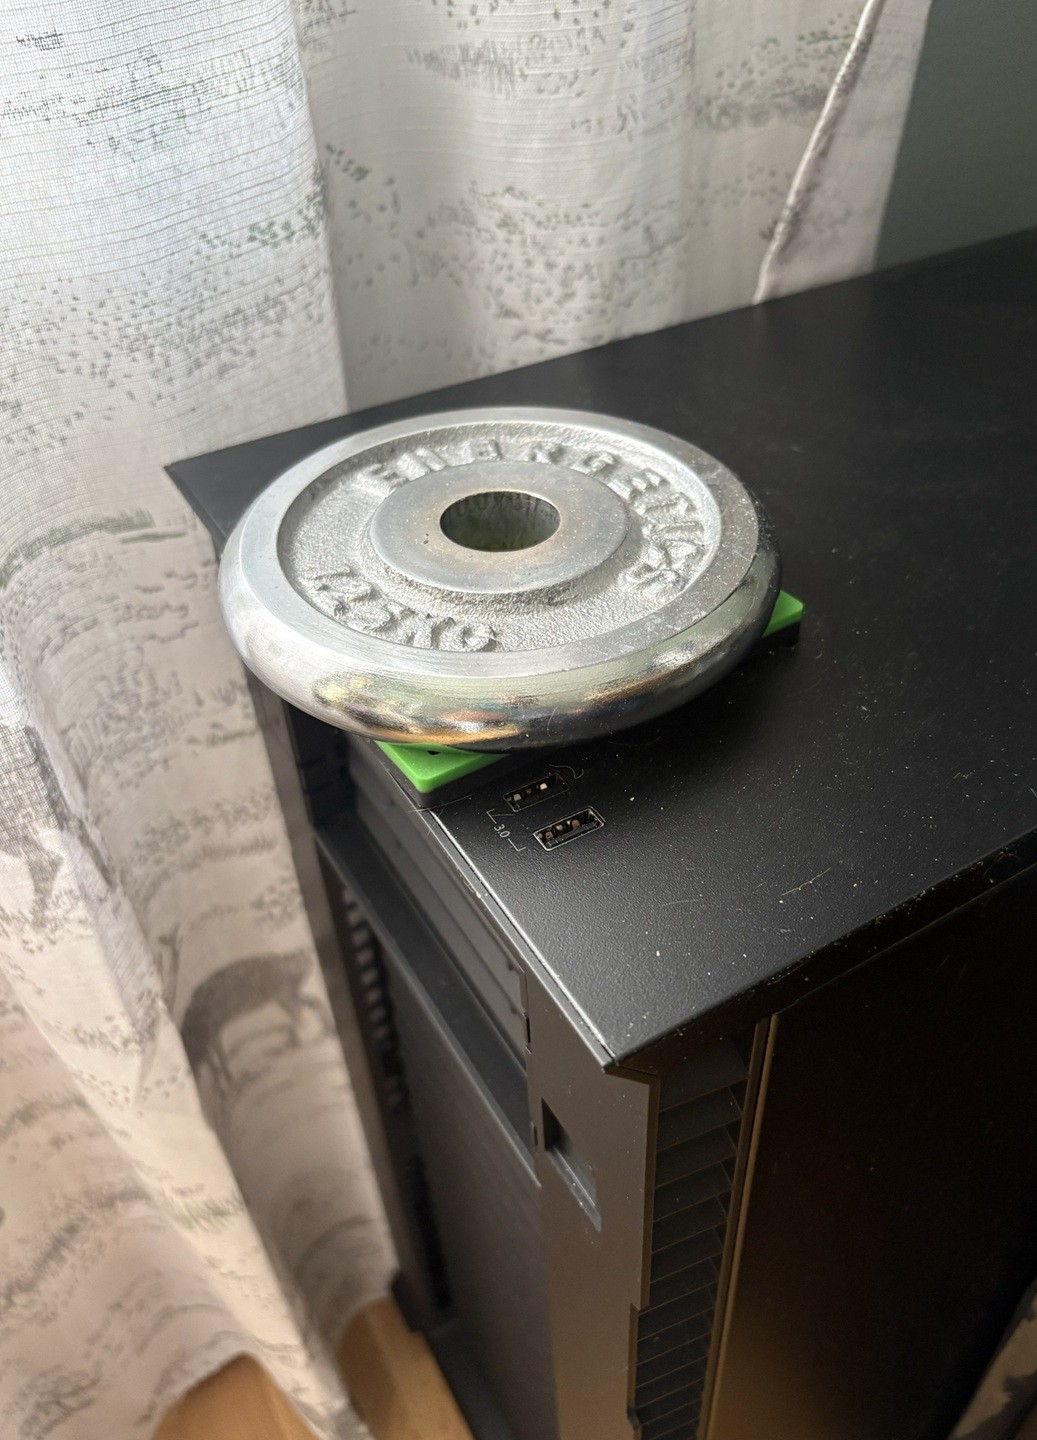
No mouse problem, but I’ve had to take measures to prevent cat-related downtime. Cats and power-button at the top is not a good combination.
I would guess that the key difference is that vibe coded apps can get to a more or less working state a lot quicker, while other apps are likely to be abandoned before it’s done.
Though in either case I’d always be careful with new projects. If it’s just a single guy that’s been working on something for less than a year and only have a handful of GitHub stars, I probably wouldn’t install it.

That would be a reasonable expectation, but I want to remember this being talked about as a revolution for internet in the US; how much better it would be compared to shitty cable providers and how you would get Gigabit speeds without having to run fibre.
Sure, it looked impressive early on, but a wireless system like this will always degrade the more customers they get.
To be fair, the network being crushed by high demand is extremely unsurprising. Cellular networks have always had this problem in dense areas, where it’s no way you’re reaching the advertised speed. This is mainly due to the available channels being shared by everyone in a relatively large area, connected to the same cell. Which is mitigated somewhat by setting up more cells with shorter range for a higher cell density in cities.
How could a satellite based network ever scale? Where you have what, a handful available cells to cover an entire state?
That doesn’t make much sense, how is a completely different infrastructure going to help their capacity issues? Unless the plan is to pivot from satellite to 5G or something
That kind of is the proper way to handle this. You don’t want to hint bad actors where to look and give people some time to update.