

4·
4 days agoThat would be great. Though I’ve had that not work as expected at the beginning of 2026, but maybe you are right.
That would be great. Though I’ve had that not work as expected at the beginning of 2026, but maybe you are right.
Note that you are likely leaking a list of all your subdomains in certificate transparency logs. Some users might not want that to happen, in that case using a wildcard certificate can help, but it’s either more tedious to set up (generating the cert outside of caddy) or less readable (using a Caddyfile with a single domain block for the wildcard containing a handle block per subdomains).
I’m not saying that’s great news, but it doesn’t sound like the self destruction move that some OSS companies have done recently. I wouldn’t migrate away just because of that change. In the end, they have to find a sustainable mode of operation.
As always, people overreacting in the comments (of the linked forum). So the current plan is that the core remains OSS, but upcoming features are partially not. To me that sounds similar to Chrome’s or VSCode’s approach.
Ah, right its stored as (rather basic) html instead of markdown.
I love ghost’s UI and feature set.
What complex data format are you taking about? Last time I checked, it was plain markdown in a database (even supporting sqlite).
What I’d recommend though, is coupling it with a static site generator and only using the ghost server for the administration / authoring (guides). That way, serving the blog to visitors is basically free in terms of resources (at last as low as it gets). You could even push these static builds to a CDN (yes yes, selfhost community, I’m just saying it for completeness)
It might be some hassle to set this up somehow, but you could even have the container stopped unless you actively need it. You could even run the server application on your computer instead of the server, unless you want to access is from a smartphone/tablet.
If you really want an alternative to Ghost and don’t need user management and an online WYSIWYG editor, you could go straight to an SSG and feed itraw it markdown files.
That puts me in an embarrassing spot, but you are probably right 😰
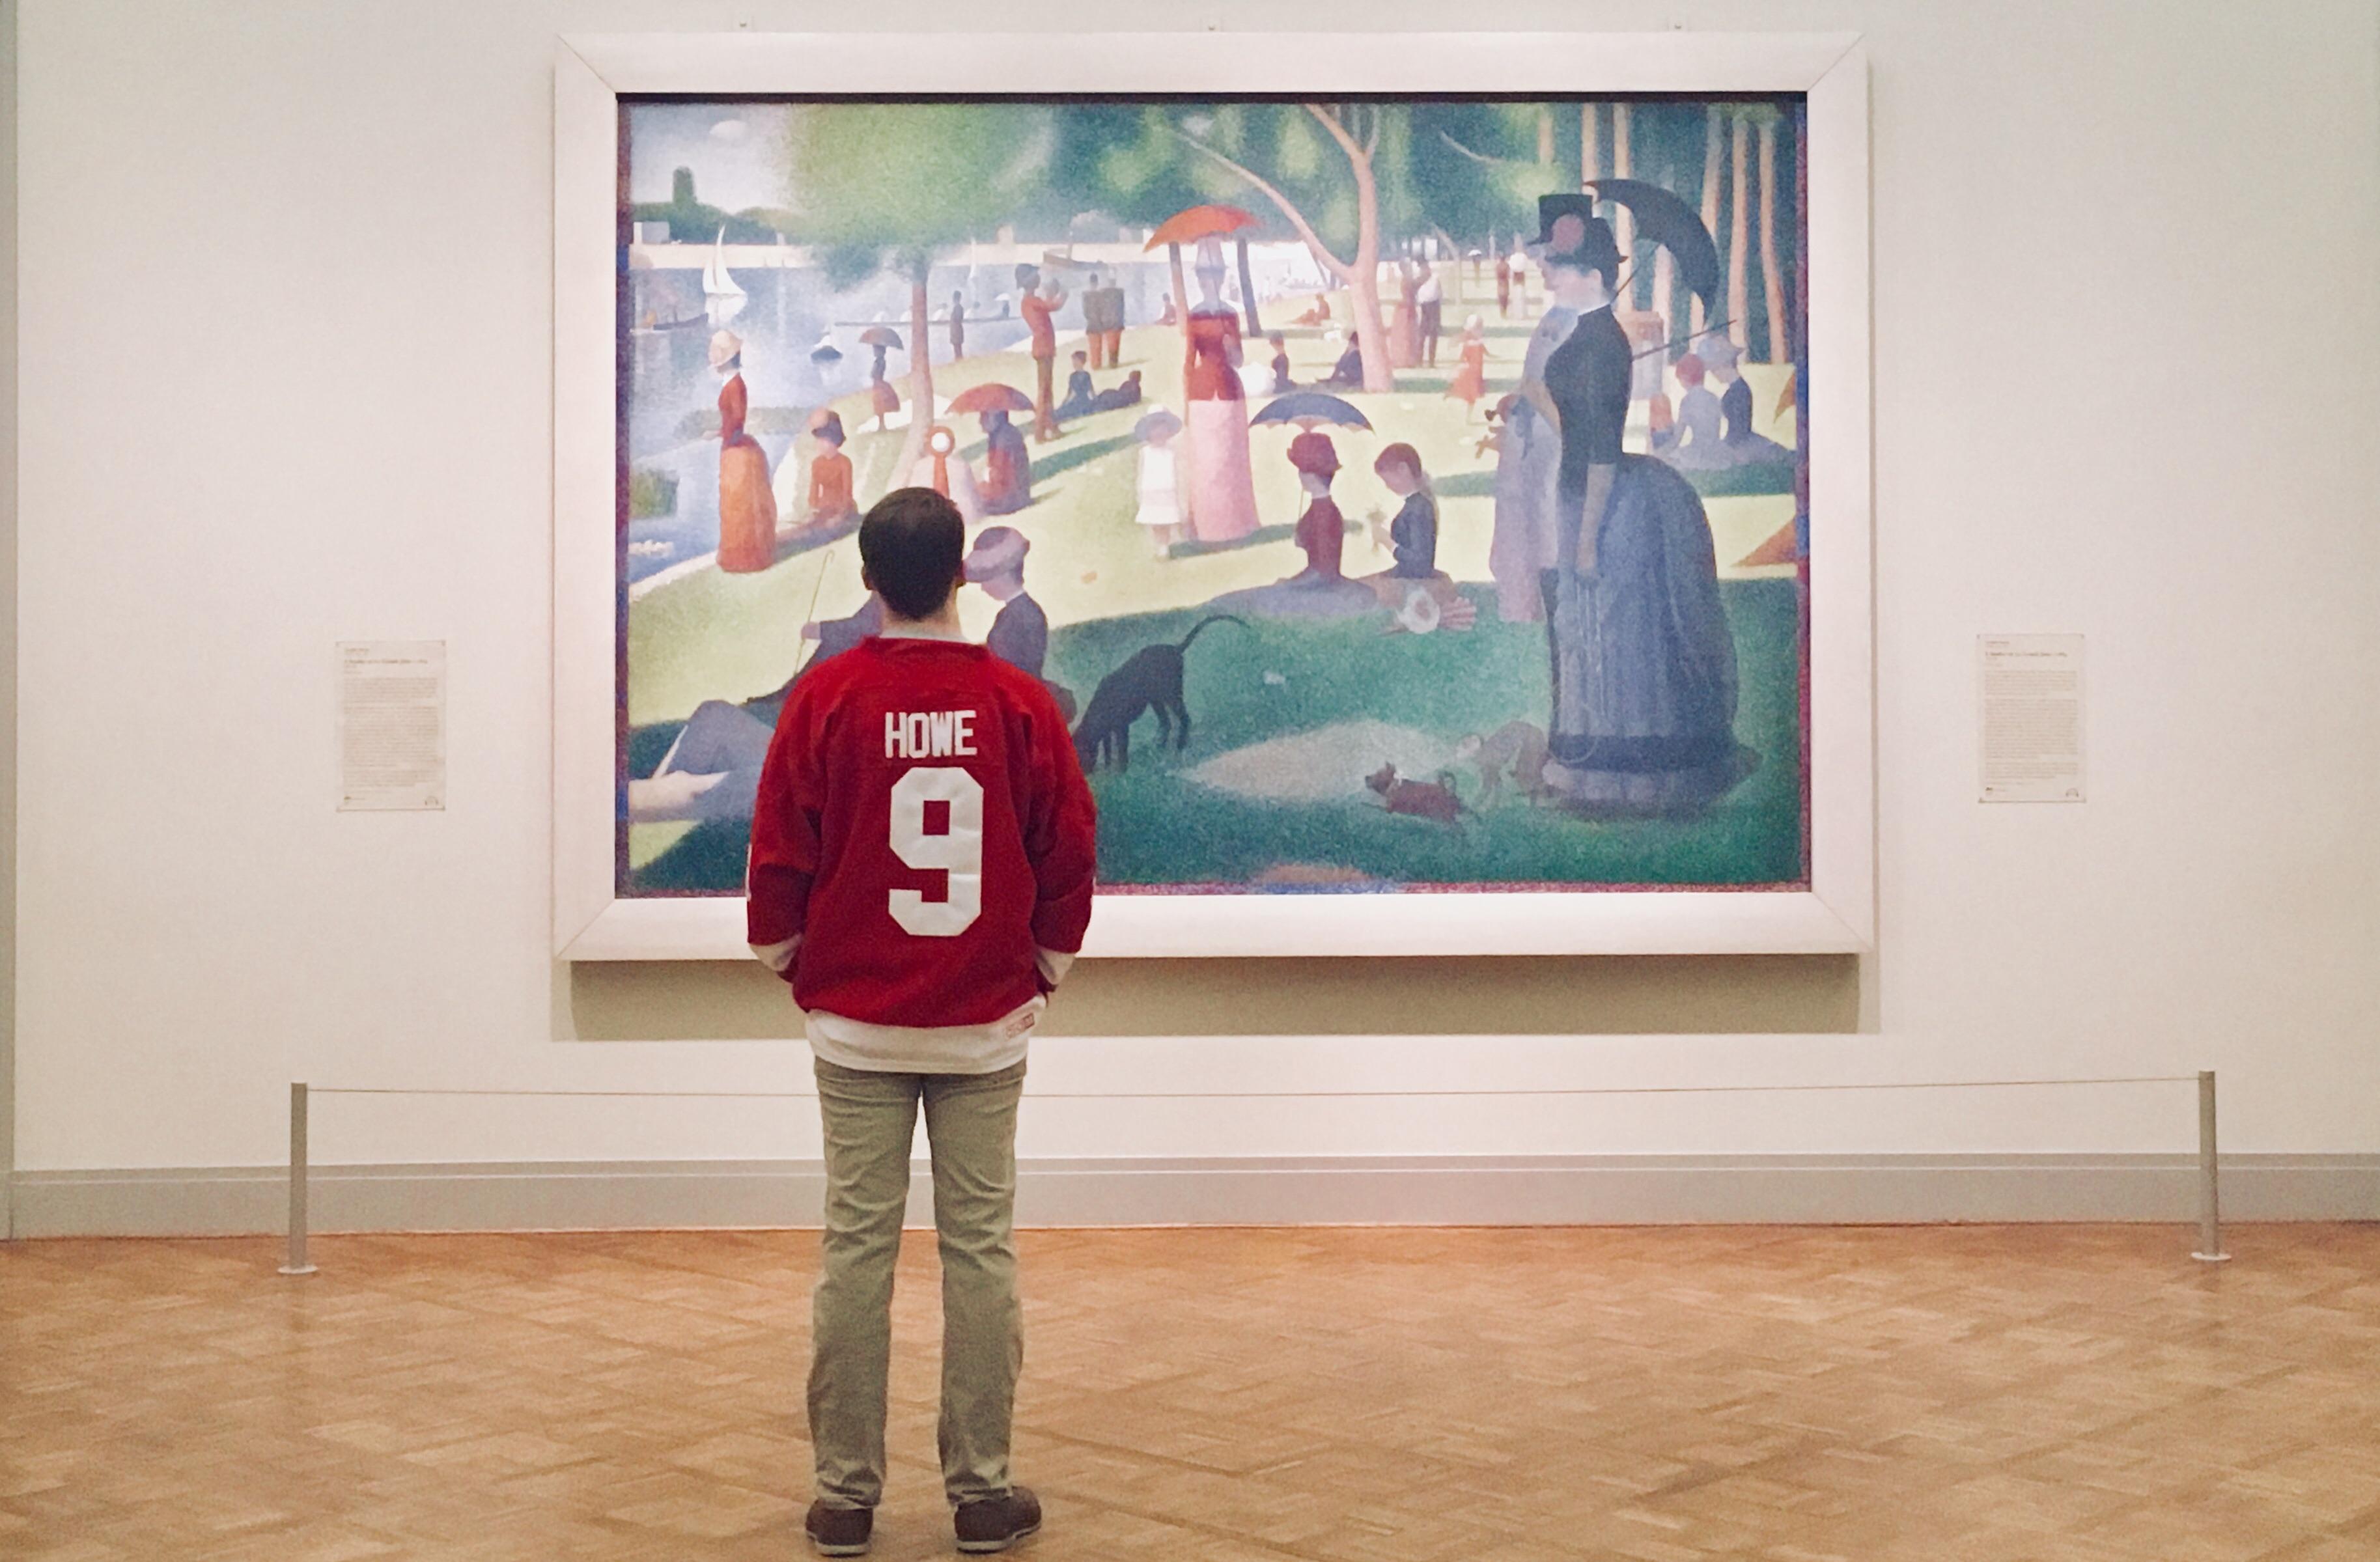
I like how accentuated the pointillism in this painting is.
Wow, those are some intense colors, having them mixed looks awesome!
You can use crowdsec without a reverse proxy and just block offending IPs using a firewall. However, you can optionally configure a reverse proxy to enforce decisions made by crowdsec, e.g. by serving error pages or by serving captchas. See Remediation Components (formally “Bouncers”)
If you want VPN support in docker containers, I was surprised his well gluetun works with any container.
Though ironically metube is the one thing I intentionally took out of the VPN, because too baby sites I cares about blocked it and I didn’t care about VPNs too in that use case.
For basic pdf manipulation, my go to choice is NAPS2. It’s a scanner app, but you can also just import pdf. It then keys you rearrange, merge, rotate, color adjust, OCR, etc. free and open source. Windows, Linux, Mac. Multilang. Comes with a CLI. Works with password protected PDF. Almost everything you can think of.
Why do you ask what “made it look like slop” instead of being honest about it?