Okay, I’m going to reply to this message with my responses to various quoted comments from the big chain of comments which I can’t directly access from this instance, due to defederation with certain instances. I’m not going to respond to literally every message, but I hope you all know that I do appreciate you for participating in this thread and being part of a really fun and interesting chain.
Thanks for all the comments and sorry for not responding until now.
Since I can’t upvote any of the comments in that chain, to all of you I provide lots of hearts:
🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷
@OwOarchist@pawb.social
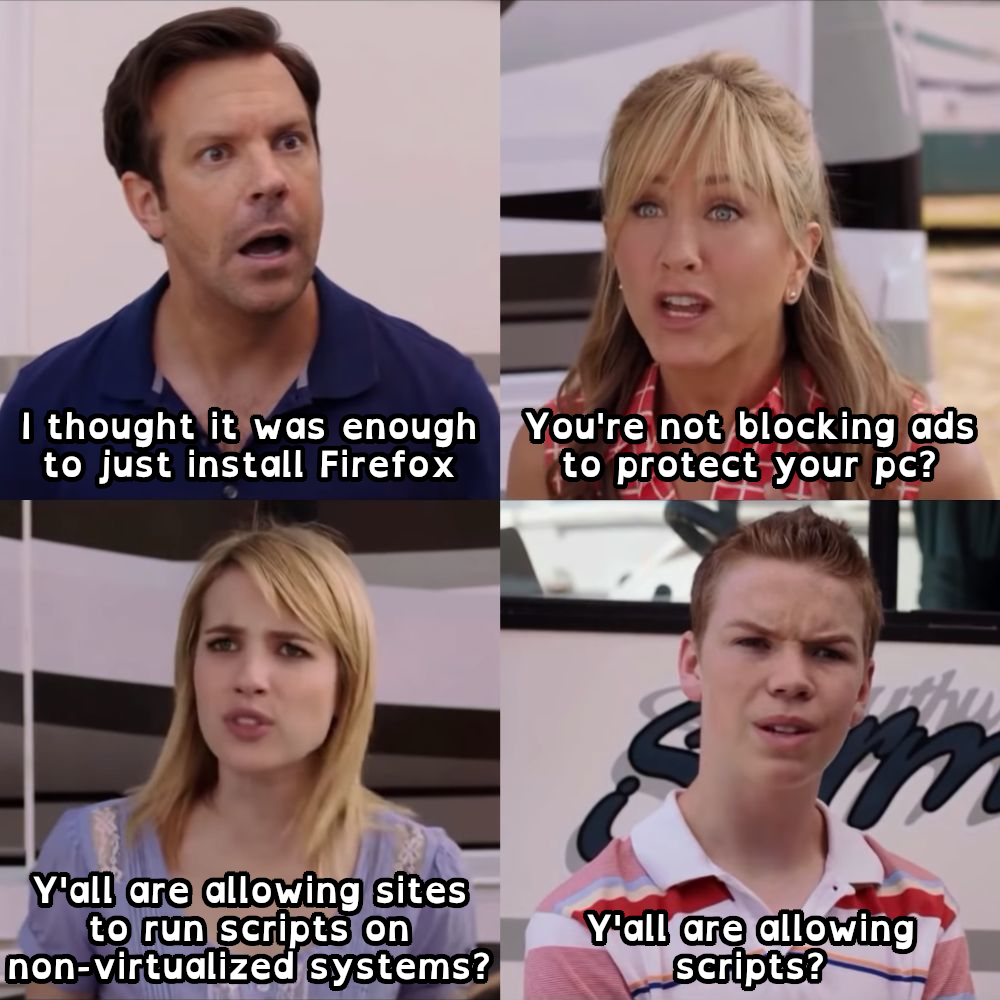
Honestly, it’s bonkers that the standard, default approach for all mainstream browsers is to let every random website in the world run any arbitrary code it wants on your computer.
This, this, 1000 times this! That is exactly how I feel and was hoping to convey.
@OwOarchist@pawb.social
Yeah, they usually attempt to sandbox it, but still. Sometimes sandboxes can be escaped. And sometimes the code can do significant harm while still inside its sandbox.
Yes, defense-in-depth includes minimizing threats rather than simply relying on protections. It shouldn’t be necessary to lower one’s shields constantly, and it’s better to avoid doing so if possible, from a security & privacy perspective.
@cley_faye@lemmy.world
Bugs exists. But JavaScript running in the browser have, theoretically, little access to anything. […]
The risk of allowing JavaScript on a website is more tied to the site data, or tracking. […]
It doesn’t mean every site needs JavaScript, but having this enabled by default is not that big of a security risk for the system. […]
This reminds me of an interesting phenomenon: Some security-oriented people praise the security of the surveillance-advertising corporation’s browser engine (chromium), while proclaiming that gecko-based browsers (firefox) are unusable due to inferior security. Yet the main security threat I see is that fucking surveillance-advertising corporation which spreads unvetted and often malicious ads around the web without a care in the world.

Okay, I’m going to reply to this message with my responses to various quoted comments from the big chain of comments which I can’t directly access from this instance, due to defederation with certain instances. I’m not going to respond to literally every message, but I hope you all know that I do appreciate you for participating in this thread and being part of a really fun and interesting chain.
Thanks for all the comments and sorry for not responding until now. Since I can’t upvote any of the comments in that chain, to all of you I provide lots of hearts: 🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷🩷
This, this, 1000 times this! That is exactly how I feel and was hoping to convey.
Yes, defense-in-depth includes minimizing threats rather than simply relying on protections. It shouldn’t be necessary to lower one’s shields constantly, and it’s better to avoid doing so if possible, from a security & privacy perspective.
This reminds me of an interesting phenomenon: Some security-oriented people praise the security of the surveillance-advertising corporation’s browser engine (chromium), while proclaiming that gecko-based browsers (firefox) are unusable due to inferior security. Yet the main security threat I see is that fucking surveillance-advertising corporation which spreads unvetted and often malicious ads around the web without a care in the world.